Quote in 48 hours
Scope your HIPAA pentest
§164.308(a)(8) evidence. PHI-safe testing. Quote in 24 hours.
TL;DR
The proposed HIPAA Security Rule update would require vulnerability scanning every six months and a full penetration test every 12 months for every system touching ePHI.
It is still proposed (Dec 2024 NPRM), with final action now targeted around 2027. The direction is set and OCR is already enforcing in these areas.
MSPs serving healthcare are business associates, directly liable, and the proposal would give BAAs teeth through annual verification of safeguards.
You can deliver audit-ready testing under your own brand without hiring senior pentesters.
9 min read · Updated July 2026
The proposed update to the HIPAA Security Rule would require every organization handling ePHI to run vulnerability scans every six months and a full penetration test every year. If you are an MSP serving healthcare clients, that requirement lands on you and your clients at the same time. Here is what is changing, why it flows through your service contracts, and how to deliver audit-ready testing without standing up an offensive security team.
What is actually changing
On December 27, 2024, the HHS Office for Civil Rights published a Notice of Proposed Rulemaking (NPRM) that would be the biggest update to the HIPAA Security Rule since 2003. It is still proposed, not final. The comment period closed in March 2025, and the latest federal agenda points to a final decision around 2027. But the direction is set, and OCR is already enforcing in these areas.
Two proposed changes matter most for anyone who does security testing:
Vulnerability scanning every six months. Automated scanning of all systems that create, receive, maintain, or transmit ePHI, at least twice a year.
Penetration testing every 12 months. A full pentest of ePHI systems at least annually, run by qualified professionals, with written documentation of findings and corrective actions. Higher-risk environments may need it more often.
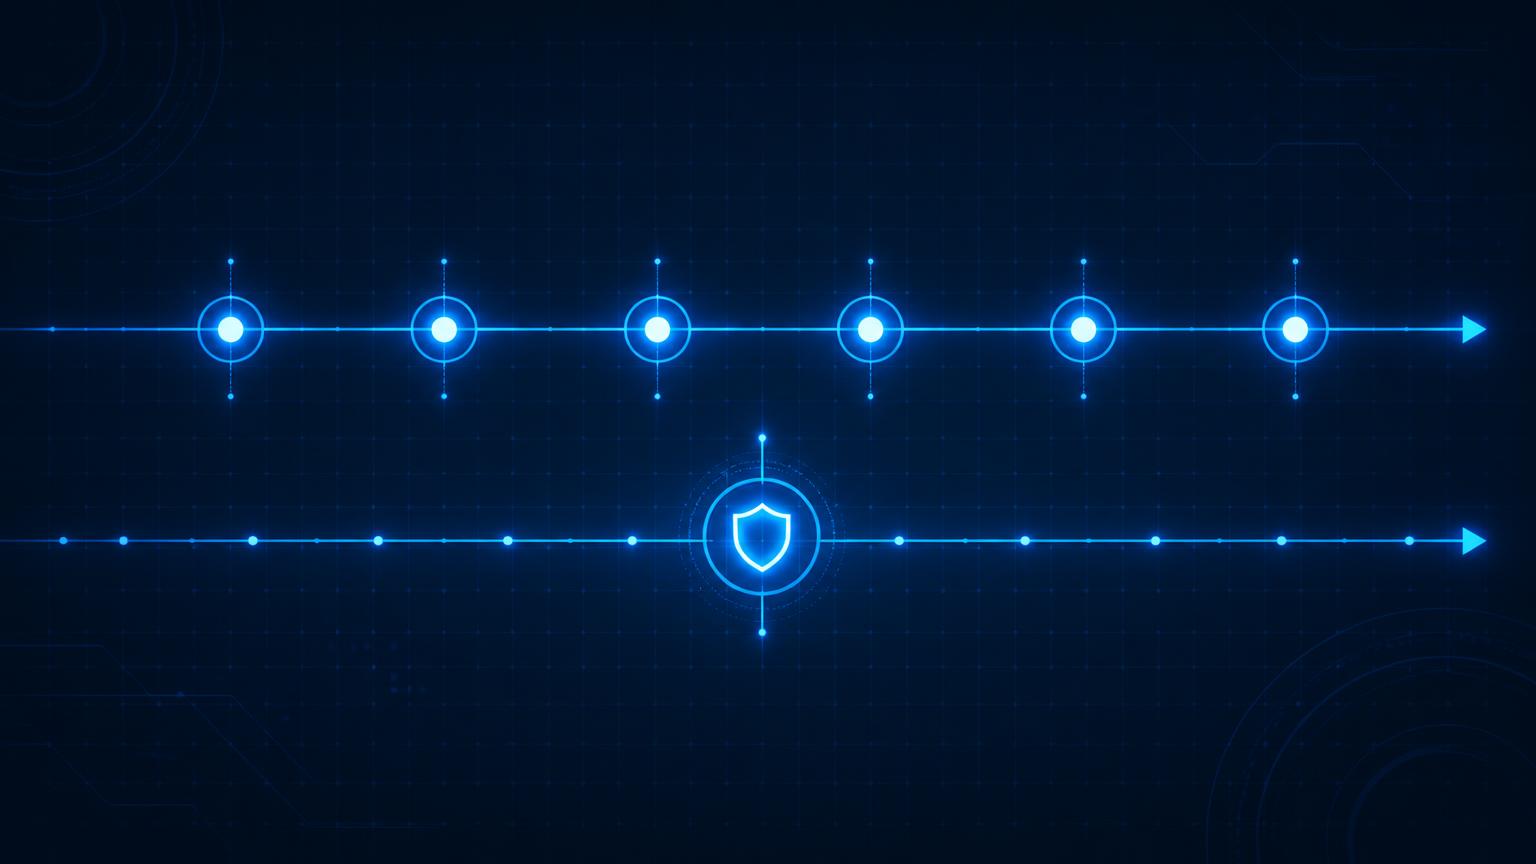
The proposed cadence: scan every six months, pentest every 12 months, both documented.
There is a bigger structural shift underneath these. The proposed rule removes the old "addressable" versus "required" distinction. Today, a smaller practice can document why a control like MFA does not fit its environment and move on. Under the proposal, that flexibility mostly disappears. Testing, MFA, encryption, and network segmentation move from nice to have to do it and prove it.
The point for MSPs: testing that used to be optional or best-effort becomes a documented compliance control your healthcare clients have to show an auditor. For the underlying requirement detail, see our HIPAA penetration testing guide and the breakdown of what the 2025 NPRM actually says.
Why this lands on the MSP, not just the client
If your MSP manages IT for a hospital, clinic, dental group, behavioral health practice, health plan, or any organization touching PHI, you are a business associate under HIPAA. That is not a gray area. Business associates are directly liable, and OCR has the settlements to prove it.
In 2025, OCR settled with a medical billing company (a business associate, not a covered entity) for $3 million after a ransomware attack exposed the data of 585,000 people. The central finding was a missing risk analysis.
OCR's recent enforcement years have been among the most active on record, and risk-analysis and business-associate failures show up again and again.
The proposed rule tightens the screws on the MSP relationship specifically:
BAAs get teeth. A signed Business Associate Agreement will not be enough. The proposal would require BAAs to name the specific technical safeguards you have in place and require annual verification that they are actually working. Testing is how you generate that proof.
24-hour breach clock. Business associates would have to notify the covered entity within 24 hours of activating an incident response plan, down from the current "without unreasonable delay." Finding problems before an attacker does becomes a lot more valuable.
So when the rule says annual penetration testing of ePHI systems, your healthcare clients are going to look at their MSP to deliver it, or to prove the MSP's own environment passed one. Either way, it is your problem to solve.
The gap most MSPs are sitting on
Here is the honest part. Most MSPs are excellent at RMM, backup, patching, and endpoint security. Very few run a real offensive security practice. Penetration testing is a different discipline: it needs senior testers, exploitation rather than scanning, and reports written in the language an auditor actually accepts.
The usual options have not been great:
Build it in-house. Hiring senior pentesters is slow and expensive, and a boutique practice is hard to keep utilized across a handful of healthcare clients.
Refer it out to a traditional firm. They charge $30K to $150K+ per engagement and take four to eight weeks. That price and timeline do not fit an SMB healthcare client on a compliance deadline, and you hand the relationship and the margin to someone else.
Pass a scanner off as a pentest. A vulnerability scan is not a penetration test, and under the proposed rule they are listed as two separate requirements. Auditors know the difference.
There is a cleaner path: make testing a service you deliver under your own brand, powered by someone who does only this.
How StealthNet closes the gap
StealthNet AI is AI-native penetration testing. Autonomous AI agents discover and exploit vulnerabilities at machine speed, and US-based senior testers validate every finding. You get the depth of a manual pentest with the speed and price that fit an SMB healthcare budget.
For the HIPAA use case specifically:
Continuous validation plans that match the rule. Instead of a one-off test, our annual plans build in scanning every six months and a full penetration test each year, which maps directly to what the proposed rule asks for. Your clients stay covered year-round, not just the week of the audit.
Hybrid AI and human pentesting, from $5,000. Audit-ready reports in 5 to 7 days instead of the four to eight weeks a traditional firm takes. Findings are mapped to the HIPAA Security Rule so your client's auditor can use the report directly.
The report is the proof. Documented findings and corrective actions are exactly the evidence the proposed BAA verification standard is asking for. That is compliance evidence, not just a security exercise.
No enterprise price tag. Traditional firms charge $30K to $150K+. We run 80%+ cheaper, which is what makes it viable to offer testing to a 20-person clinic instead of only a hospital system.
See how the scope and reporting work on our HIPAA penetration testing page.
Do it under your own brand: the partner program
Co-branded or fully white-label: your client sees your brand on the report.
You do not have to build an offensive security team to offer testing. Our partner program lets MSPs resell or white-label StealthNet, so testing becomes a line item on your invoice, not a referral you lose control of.
Resell or white-label. Deliver the report co-branded or fully under your brand. Your client sees you as the security partner who solved their HIPAA testing requirement.
Real margin. Partners buy at roughly 25% off retail, so recurring continuous-validation plans across your healthcare book become a new revenue line, not a pass-through.
Zero standing overhead. No senior-tester payroll, no scheduling boutique engagements, no utilization risk. You scope, we test, you keep the relationship.
Fast enough to sell. A 24-hour quote and a 5 to 7 day turnaround means you can answer a client's "we need a pentest for the audit" without a month of runway.
The pitch to your clients writes itself: the HIPAA rule is raising the bar on testing, and you already have it handled.
What to do now, while the rule is still proposed
You do not have to wait for the final rule. The enforcement trajectory is already here, and getting ahead of it is a sales motion, not just a compliance one.
List your healthcare clients handling PHI. That is your scope, and your opportunity list.
Check your BAAs. Confirm one is signed with every PHI client, and start noting which technical safeguards you can actually prove.
Baseline the testing gap. Which of those clients has ever had a real penetration test, not just a scan? That is your near-term pipeline.
Pick a delivery model. In-house, referral, or partner-powered. If you want testing as a branded, recurring service without the overhead, talk to us.
Lead the conversation. Tell your healthcare clients what is coming before a competitor does. "The HIPAA Security Rule is adding annual pentesting, and we have you covered" is a strong renewal and upsell hook.
Frequently asked questions
Does HIPAA require penetration testing?
Not yet, explicitly. The HIPAA Security Rule in force today does not set a specific testing schedule. The proposed 2024/2025 update to the rule would expressly require penetration testing of ePHI systems at least once every 12 months, plus vulnerability scanning at least every six months. It is still a proposed rule, but OCR already treats a documented risk analysis, which testing supports, as a baseline enforcement expectation.
How often would HIPAA require vulnerability scanning and pen testing?
Under the proposed rule: automated vulnerability scanning at least every six months, and a full penetration test at least every 12 months, or more often if the organization's risk analysis calls for it. Both must be documented, with findings and corrective actions on record.
Are MSPs responsible for penetration testing under HIPAA?
If an MSP creates, receives, maintains, or transmits PHI for a healthcare client, it is a business associate and is directly subject to the Security Rule. That means the MSP is on the hook for testing its own ePHI systems, and healthcare clients increasingly expect their MSP to deliver or coordinate testing for them. The proposed rule would also require business associates to prove their safeguards are working through annual verification.
Can an MSP outsource HIPAA penetration testing?
Yes. Most MSPs do not run an in-house offensive security team, so they partner with a specialist. StealthNet's partner program lets MSPs resell or white-label audit-ready HIPAA penetration testing, so the MSP keeps the client relationship and the margin without hiring senior testers. Reports are mapped to the HIPAA Security Rule and delivered in 5 to 7 days.
Is a vulnerability scan the same as a penetration test?
No. A scan is automated detection of known weaknesses. A penetration test actively exploits vulnerabilities to show real business impact, the way an attacker would. The proposed HIPAA rule lists them as two separate requirements, so passing a scan off as a pentest will not satisfy an auditor.
How much does HIPAA penetration testing cost through StealthNet?
Hybrid AI and human pentests start at $5,000, well below the $30K to $150K+ traditional firms charge. Continuous validation plans that bundle six-month scans and an annual pentest are priced as annual subscriptions, and partners buy at wholesale for resale. Get a fixed-fee quote within 24 hours.
The rule is changing. Get ahead of it with your clients.
Offer audit-ready HIPAA penetration testing under your own brand, with continuous validation that matches what the proposed rule asks for. No offensive security team required. Become a partner or get a pentest quote, or book a 30 minute chat with us at https://calendly.com/stealthnet/discovery-call-partnerships.
Sources
HHS OCR, HIPAA Security Rule NPRM fact sheet (hhs.gov)
Kaseya, "HIPAA compliance for MSPs: what's changing and what you must do now" (May 2026)
HIPAA Journal, "Proposed Changes to the HIPAA Security Rule for Business Associates"
Accountable, "HIPAA NPRM: New Vulnerability Scanning Requirements Explained"
OMB Unified Agenda RIN 0945-AA22 (final action target ~2027)