Quote in 48 hours
Scope your HIPAA pentest
§164.308(a)(8) evidence. PHI-safe testing. Quote in 24 hours.
HIPAA penetration testing is the offensive-security exercise a covered entity or business associate runs against every system that creates, receives, maintains, or transmits electronic protected health information (ePHI). It proves which weaknesses in that boundary an attacker could actually exploit, and it is fast becoming the single most requested piece of evidence in OCR investigations and enterprise BAA reviews.
This guide covers what HIPAA actually requires today, what the 2025 NPRM changes, how often you should run a HIPAA pentest, what a compliant report has to contain, and how to scope an engagement that will hold up in front of an auditor.
Does HIPAA require penetration testing?
The short answer in 2026: effectively yes, and explicitly yes if the 2025 NPRM is finalized as written.
The 2003 Security Rule at 45 CFR §164.308(a)(1)(ii)(A) requires an "accurate and thorough assessment of the potential risks and vulnerabilities" to ePHI, and §164.308(a)(8) requires periodic technical evaluation. The phrase "penetration test" does not appear, but OCR's own guidance, its resolution agreements, and every serious auditor treat a validated pentest as the primary way to satisfy those clauses. Vulnerability scans alone are not enough because they do not prove exploitability.
On December 27, 2024, HHS published a Notice of Proposed Rulemaking updating the Security Rule for the first time in over 20 years. The proposal is explicit:
- Annual penetration testing of relevant electronic information systems, called out as a required specification under §164.308.
- Vulnerability scanning at least every six months.
- Elimination of the "addressable" vs "required" distinction, so almost every specification becomes mandatory.
- Written technical asset inventory and network map, refreshed annually and after material changes.
The public comment window closed in March 2025 and a final rule is expected in late 2026 or 2027. Enterprise customers, cyber insurers, and BAA counterparties are already writing the proposed HIPAA penetration testing requirements into contracts, so most regulated teams are moving now rather than waiting for the final rule.
What HIPAA penetration testing covers
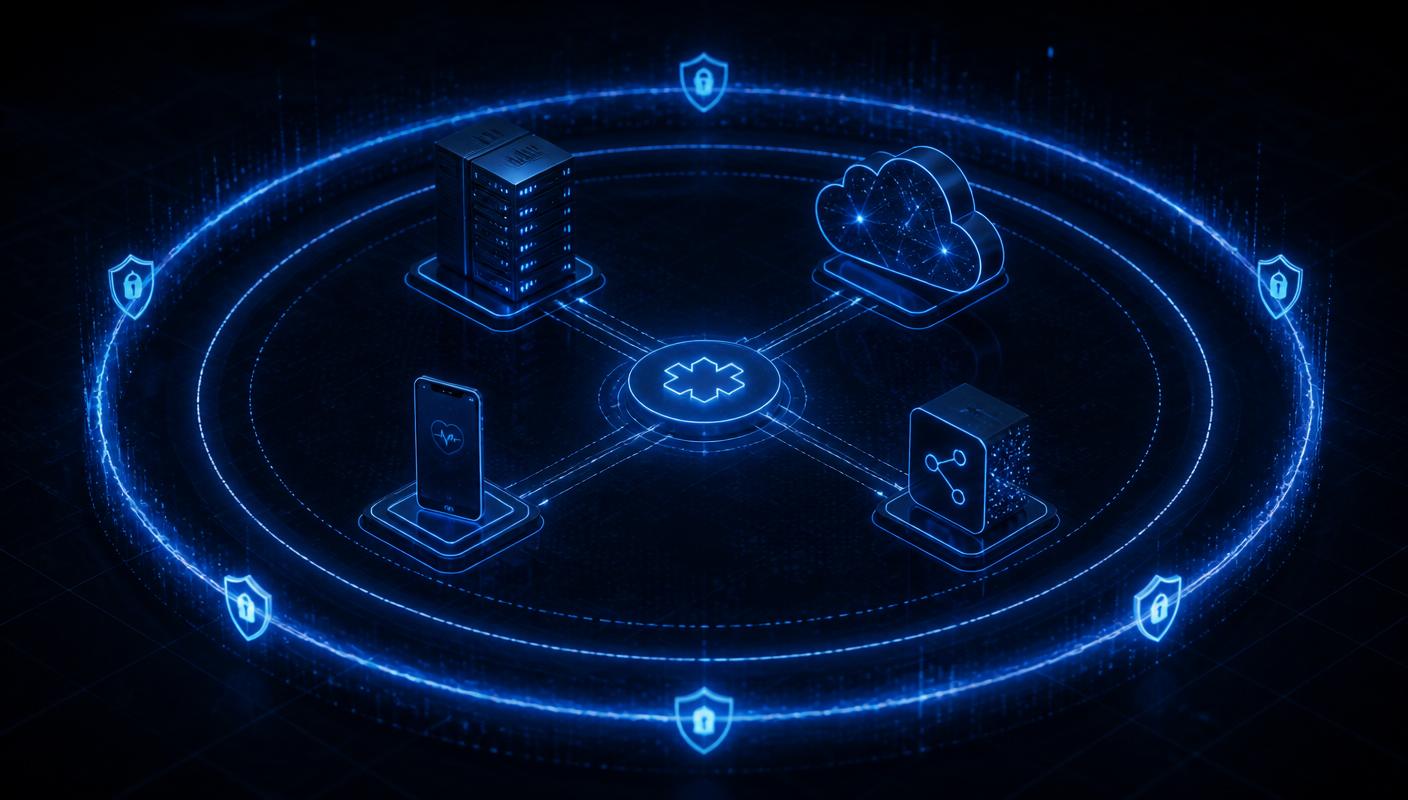
The scope is defined by ePHI, not by IP range. Anywhere ePHI is created, received, maintained, or transmitted is in scope. In a typical 2026 healthcare or health-tech environment that includes:
- External attack surface: patient portals, provider portals, marketing sites that collect PHI, telehealth endpoints.
- APIs: FHIR endpoints, EHR integrations, billing and claims APIs, third-party partner integrations.
- Internal network: segments hosting EHRs, PACS, imaging, HL7 interfaces, backup systems.
- Cloud infrastructure: AWS, Azure, or GCP accounts hosting ePHI workloads, including IAM, storage buckets, and Kubernetes clusters.
- Mobile and companion apps that handle PHI.
- Vendor and BAA-connected systems that touch your ePHI boundary.
Scoping mistakes are the number one reason HIPAA pentests fail their next audit. Excluding a "marketing" subdomain that quietly collects appointment PHI, or leaving a legacy VPN out of scope, is exactly the gap OCR looks for after a breach.
How often should you run a HIPAA pentest?
| Trigger | Recommended Cadence | Why |
|---|---|---|
| Full ePHI-boundary pentest | Annually | Explicit in the 2025 NPRM. Already the enterprise BAA default. |
| After material change | Within 30 days | New EHR module, new cloud region, new BAA partner, major refactor. |
| Vulnerability scanning | Continuous or monthly | NPRM floor is every 6 months. Modern teams run continuous. |
| After a security incident | Immediately post-remediation | OCR expects proof the exploited path is closed. |
What an OCR-ready HIPAA pentest report contains
Auditors and OCR investigators do not want a raw scanner export. A defensible HIPAA pentest report includes:
- Executive summary tied to ePHI risk, not CVSS scores in isolation.
- Explicit scope statement naming every in-scope asset, environment, and exclusion.
- Methodology referencing recognized frameworks (NIST SP 800-115, OWASP WSTG, PTES).
- Findings with proof of exploitability, screenshots or request/response pairs, and business impact in PHI-disclosure terms.
- Mapping to the HIPAA Security Rule administrative, physical, and technical safeguards each finding touches.
- Remediation guidance and retest evidence.
- Attestation and signature from a qualified human tester. Unsigned autonomous-tool output does not clear enterprise BAA reviews.
Where AI changes the equation in 2026
Traditional HIPAA pentests took four to six weeks and cost $25,000 to $75,000 per engagement, which is why most regulated teams historically tested once a year and hoped nothing changed in between. That model is breaking.
A hybrid pentest pairs autonomous AI agents that handle recon, enumeration, exploitation, and chaining with a senior tester who validates every finding, chases business-logic depth, and signs the report. The practical impact for HIPAA teams:
- Kickoff to signed report in as little as 48 hours for well-scoped ePHI boundaries.
- Continuous coverage between annual reports, so a new deploy does not blow a hole in your Security Rule posture for six months.
- Consistent methodology across engagements, which matters when OCR asks for three years of evidence.
- Lower per-engagement cost, so annual testing plus post-change retests becomes economically realistic.
The critical caveat: autonomous-only tools that emit an unsigned report will not clear a serious BAA review. The HIPAA-defensible pattern is AI agents plus a named human tester who signs.
Common HIPAA pentest scoping mistakes
- Scoping by network, not by data. If ePHI touches it, it is in scope, regardless of which subnet it lives on.
- Excluding third-party BAAs. Vendor-hosted systems processing your PHI are part of your risk analysis obligation.
- Skipping the internal network. Ransomware groups target flat internal networks precisely because external hardening has improved.
- Treating a vulnerability scan as a pentest. Scanners enumerate CVEs. Pentests prove exploitability. OCR and enterprise auditors know the difference.
- Testing once a year and calling it done. The NPRM, cyber insurers, and enterprise BAAs are all moving to continuous.
How to run a HIPAA pentest that will hold up
- Inventory ePHI first. Map every system, integration, and vendor that touches PHI. This becomes your scope.
- Pick a vendor whose report maps findings to §164.308, §164.310, and §164.312. Generic pentest reports create audit rework.
- Run a full-boundary test annually and lightweight retests on every material change.
- Retain three years of reports, remediation evidence, and retest results. OCR routinely asks for multi-year evidence during investigations.
- Layer continuous scanning underneath. Six-month gaps between HIPAA pentests are where breaches happen.
For a deeper walkthrough of the exact evidence OCR asks for and how a hybrid engagement delivers it, see our HIPAA penetration testing service page.