Quote in 48 hours
Scope your HIPAA pentest
§164.308(a)(8) evidence. PHI-safe testing. Quote in 24 hours.
What the 2003 Security Rule actually says
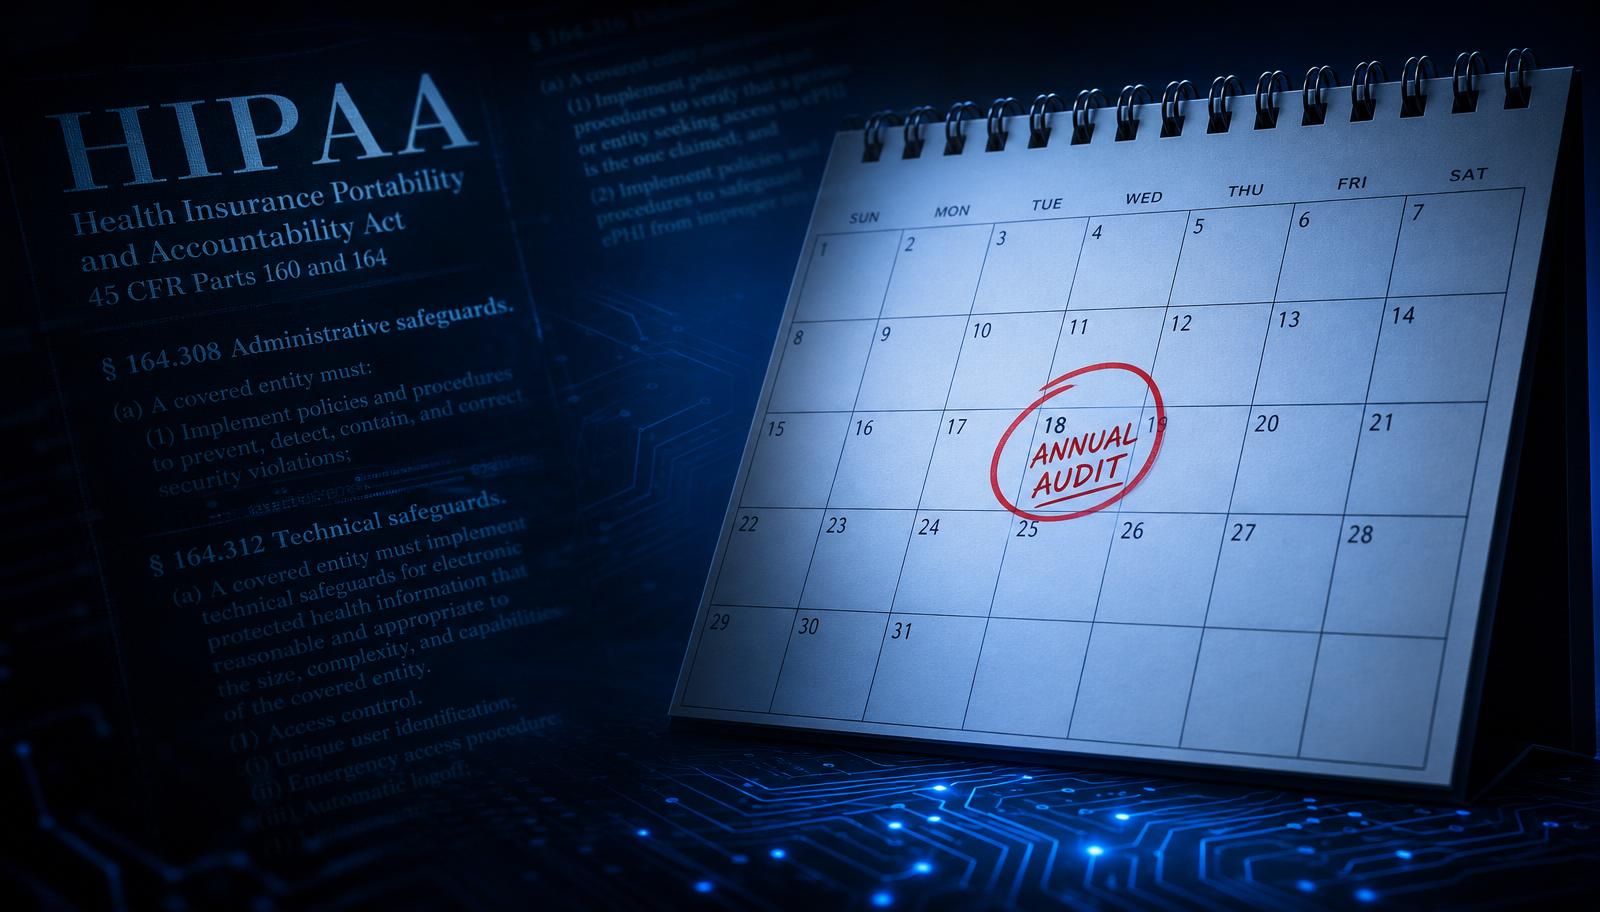
The current HIPAA Security Rule at 45 CFR §164.308(a)(1)(ii)(A) requires an "accurate and thorough assessment of the potential risks and vulnerabilities" to ePHI, and §164.308(a)(8) requires periodic technical evaluation. Neither section names "penetration testing." That single omission is the reason covered entities have argued for two decades that a vulnerability scan or a questionnaire-based SRA is enough.
OCR has never agreed with that reading. Its published guidance, its corrective action plans, and its resolution agreements consistently point to validated technical testing as the way to prove exploitability. A scanner tells you a CVE exists. A pentest tells you an attacker can reach ePHI through it. Auditors care about the second answer.
What the December 2024 NPRM changes
On December 27, 2024, HHS published a Notice of Proposed Rulemaking updating the Security Rule for the first time in over 20 years. The proposal is unambiguous about testing cadence:
- Annual penetration testing of relevant electronic information systems, written directly into §164.308.
- Vulnerability scanning at least every six months.
- Elimination of the "addressable" vs "required" distinction, so almost every specification becomes mandatory.
- Written technical asset inventory and network map, refreshed annually and after any material change.
The public comment window closed in March 2025. A final rule is expected in late 2026 or 2027, with a compliance runway that most analysts read as 180 days after publication. The direction of travel is clear: annual pentesting is being codified, not debated.
Why enterprises already require it today
Even before the final rule lands, three forces have already made annual HIPAA penetration testing table stakes:
- Enterprise BAA reviews. Health-system and payer procurement teams now put "annual third-party pentest, report available on request" directly into business associate agreements. Failing that clause loses the deal.
- Cyber insurance underwriting. Renewals in 2025 and 2026 routinely ask for the most recent pentest report and a remediation attestation. Missing evidence maps to premium increases or coverage exclusions for ransomware and PHI exfiltration.
- OCR enforcement posture. Recent resolution agreements repeatedly cite the absence of a validated technical assessment as an aggravating factor. The 2024–2025 enforcement trend is toward multi-million-dollar settlements where the missing artifact is a real pentest, not another questionnaire.
What "annual" actually means in practice
The NPRM's annual cadence is a floor, not a ceiling. A defensible 2026 program looks like:
- One full-scope pentest per year covering the entire ePHI boundary — patient portals, provider portals, APIs, cloud infrastructure, internal networks with PHI reach, and any BAAs’ connected systems.
- A targeted pentest after any material change — a new application handling PHI, a major infrastructure migration, a merger, or a significant architecture change.
- Continuous vulnerability scanning between engagements, feeding a live remediation queue rather than a once-a-year PDF.
- A written remediation attestation that closes each finding with either a fix, a compensating control, or a documented risk acceptance signed by a named owner.
Traditional firm vs. hybrid AI + human pentest
Traditional pentest firms quote 4 to 6 weeks of calendar time and $25K to $80K for a full HIPAA engagement. That model still works, but it does not scale to annual retesting across a growing ePHI footprint, and it does not fit into a 2026 procurement cycle that expects evidence in days.
Pure autonomous-tool output without a human sign-off is the pattern that most often gets pushed back on during enterprise BAA reviews. The reliable 2026 model is a hybrid pentest: AI agents run the breadth across the ePHI boundary, a senior tester validates every finding, chains exploits where they exist, and signs the report. You get real exploitability evidence, mapped to §164.308, in a fraction of the time.
Bottom line
Yes for practical purposes today, and yes explicitly once the NPRM is finalized. The teams that will have the easiest audits in 2027 are the ones who started running annual, well-scoped, human-signed HIPAA pentests in 2025 and 2026.
See our HIPAA penetration testing service page for what an OCR-ready engagement looks like end to end, or read the full HIPAA pentest requirements, frequency, and compliance guide.