    Continuous penetration testing Build it once.
    Run it all year.

    Get your next pentest signed in 48 hours. Then keep the same app tested every month after it, with a fresh signed report ready for your next audit.

    • ★★★★★ 5.0 on Capterra
    • Senior US-based testers
    • Signed report and attestation letter

    Fixed quote within 24 hours. See what year one costs

    Before year-end

    Before year-endNext year
    JFMAMJJASOND

    Build
    signed report in 48 hours (AI Pentest)

    Run
    a full AI pentest every month, a re-test on every release

    Fresh signed report,
    ready for your next audit

    A year-end pentest covers one week. Run covers every month after it.

    Every year ends the same way: a rush to get a pentest done before the audit. The report gets filed, and the app keeps shipping all year with no one testing it again.

    2 to 4 weeks

    Lead time just to start at a traditional pentest firm.

    $20K+

    What a traditional test can cost, for one point in time.

    364 days

    Of blind spots that annual testing leaves behind.

    What is continuous penetration testing?

    Continuous penetration testing is pentesting that runs all year instead of once before an audit. The same app is tested every month and on every release, fixed findings are retested, and a signed report is ready when your auditor asks. It is usually sold as penetration testing as a service (PTaaS): a subscription instead of a one-off project.

    StealthNet AI's version is Run. AI agents test your app every month, senior US-based testers validate the findings, and your annual report reflects a year of testing, not one week.

    Annual pentest vs vulnerability scanning vs continuous penetration testing
    QuestionAnnual pentestVulnerability scanningContinuous pentesting with StealthNet AI Run
    How often your app is testedOnce a year, for about a weekOften, for known issues onlyA full AI pentest every month, plus a re-test on every release
    Findings exploited and validated by a personYes, during the test windowNoYes. Senior testers review every quarter and run the annual test
    Signed report for your auditorYes, once a yearNo. Scan output is not a pentest reportYes. A dated, full-scope annual test and signed report, timed to your audit window
    Longest gap between testsUp to 364 daysLogic and access-control flaws go untestedAbout a month, less with release re-tests
    Lead time and price2 to 4 weeks to start, $20K+ per testRuns on its own, no pentest evidenceStarts from your Build. From $7,500 per year

    How it works

    Three steps. One fixed number per line, agreed before any work starts.

    From first call to signed report

    1. Scoping call

      30 minutes with our team

    2. Within 24 hours

      Your fixed quote

    3. 48 hours from kickoff

      Signed AI Pentest report

    4. Every month after

      Run tests the same app

    1. 1

      Scope it on a 30-minute call

      Tell us what the app is and what the audit needs. You get a fixed quote within 24 hours.

      • 30-minute call
      • Fixed quote within 24 hours
    2. 2

      Build: this year's pentest, signed

      AI agents and senior US-based testers test your app. An AI Pentest takes 48 hours from kickoff and a Hybrid takes 3 to 5 days, report included. You keep everything it produces.

      • Signed report
      • Attestation letter
      • Your test playbook
      • One retest within 360 days
    3. 3

      Run: the same app, tested every month

      Run begins when your Build report is delivered and tests against the playbook the Build produced. Ahead of each annual audit we run a dated, full-scope test and you get a fresh signed report, so you never buy a second Build for the same app.

      • A full AI pentest every month
      • A re-test on every release (up to four releases a month)
      • Unlimited retests on findings
      • Senior tester reviews every quarter

    A Build you keep.
    A Run that keeps going.

    Penetration testing pricing, published up front. Every StealthNet AI program starts with a Build. Add Run to keep that app tested every month, with senior tester hours every quarter.

    Build

    One-time fee. The first engagement.

    A pentest of your app that stands on its own. Pick the depth your audit needs.

    • AI Pentest

      A single small scope: 1 role, one target

      AI agents plus 2 hours of senior validation. 48 hours from kickoff, report included.

      from $3,500

    • Hybrid

      Business logic, auth roles and regulated evidence

      AI agents plus senior manual testing. 3 to 5 days from kickoff. Built for FDA, PCI and HIPAA evidence. FDA 510(k) scopes are typically $5,000 to $10,000.

      from $5,000

    • Program

      Multiple apps, enterprise and custom scopes

      Manual-led testing on a custom threat model, executive readout. Scoped and fixed within 24 hours.

      from $12,000

    Every Build includes

    • Signed report
    • Attestation letter
    • Your test playbook
    • One retest within 360 days
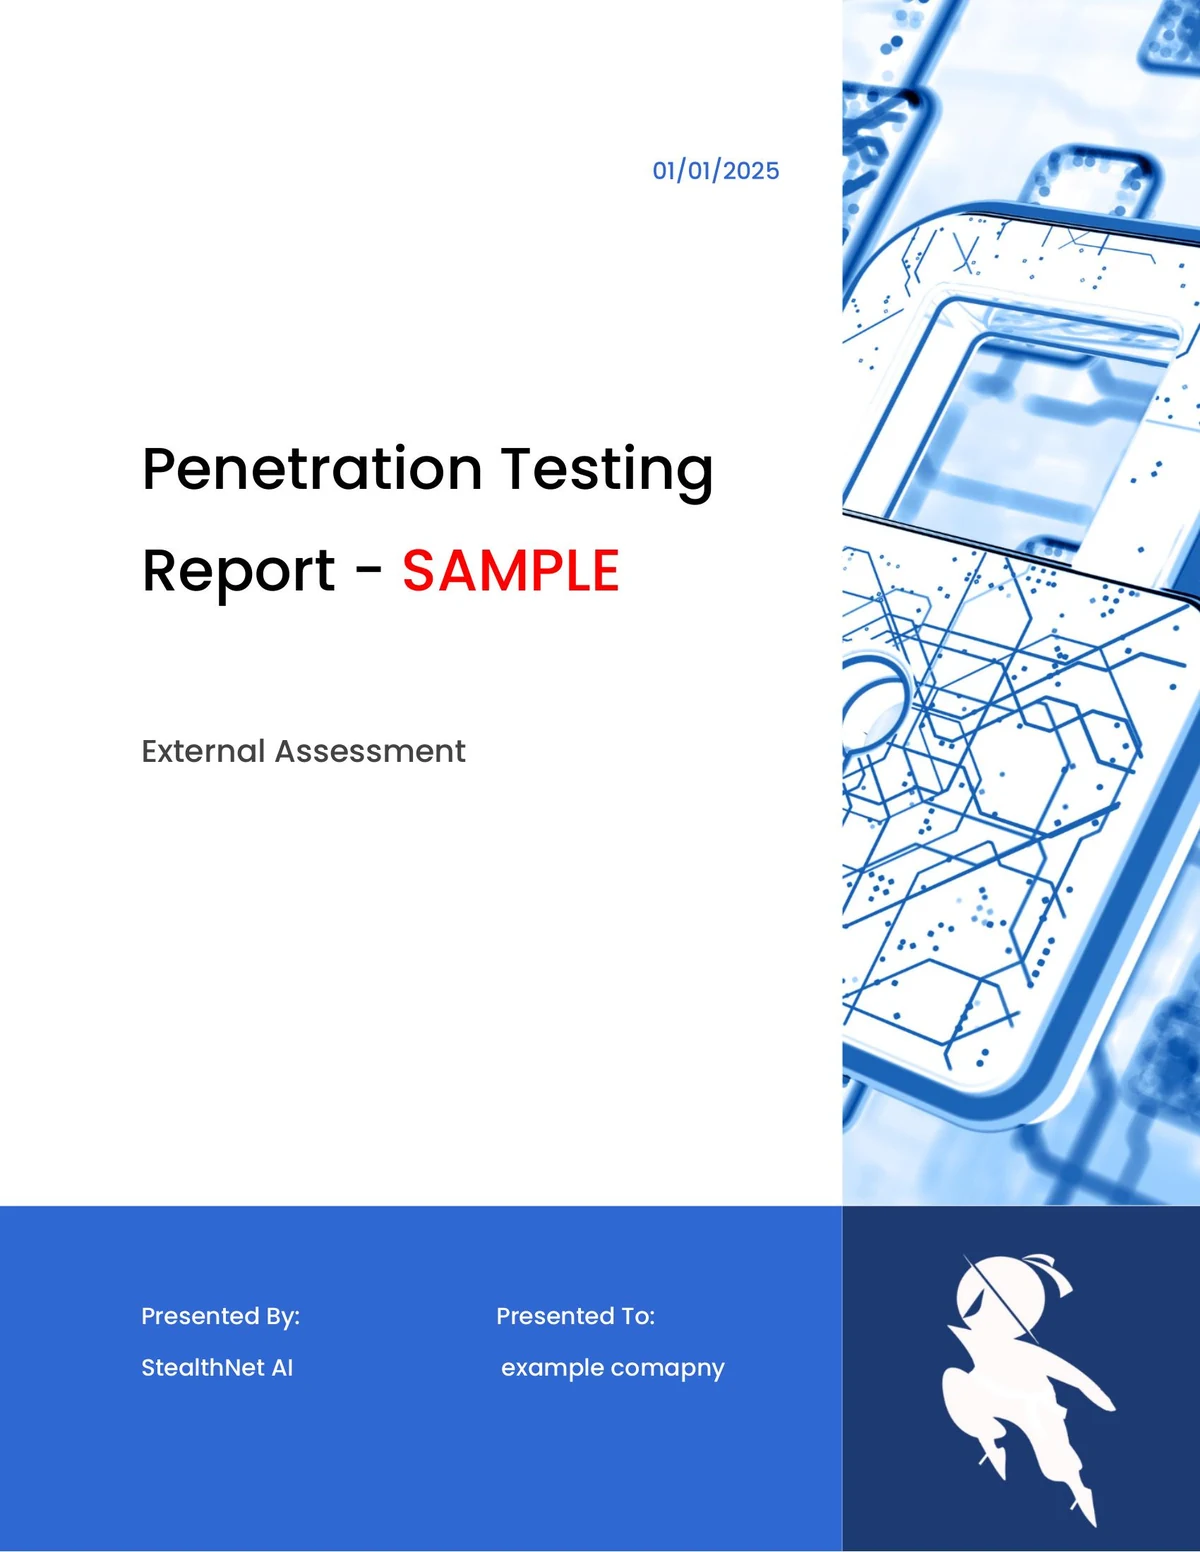
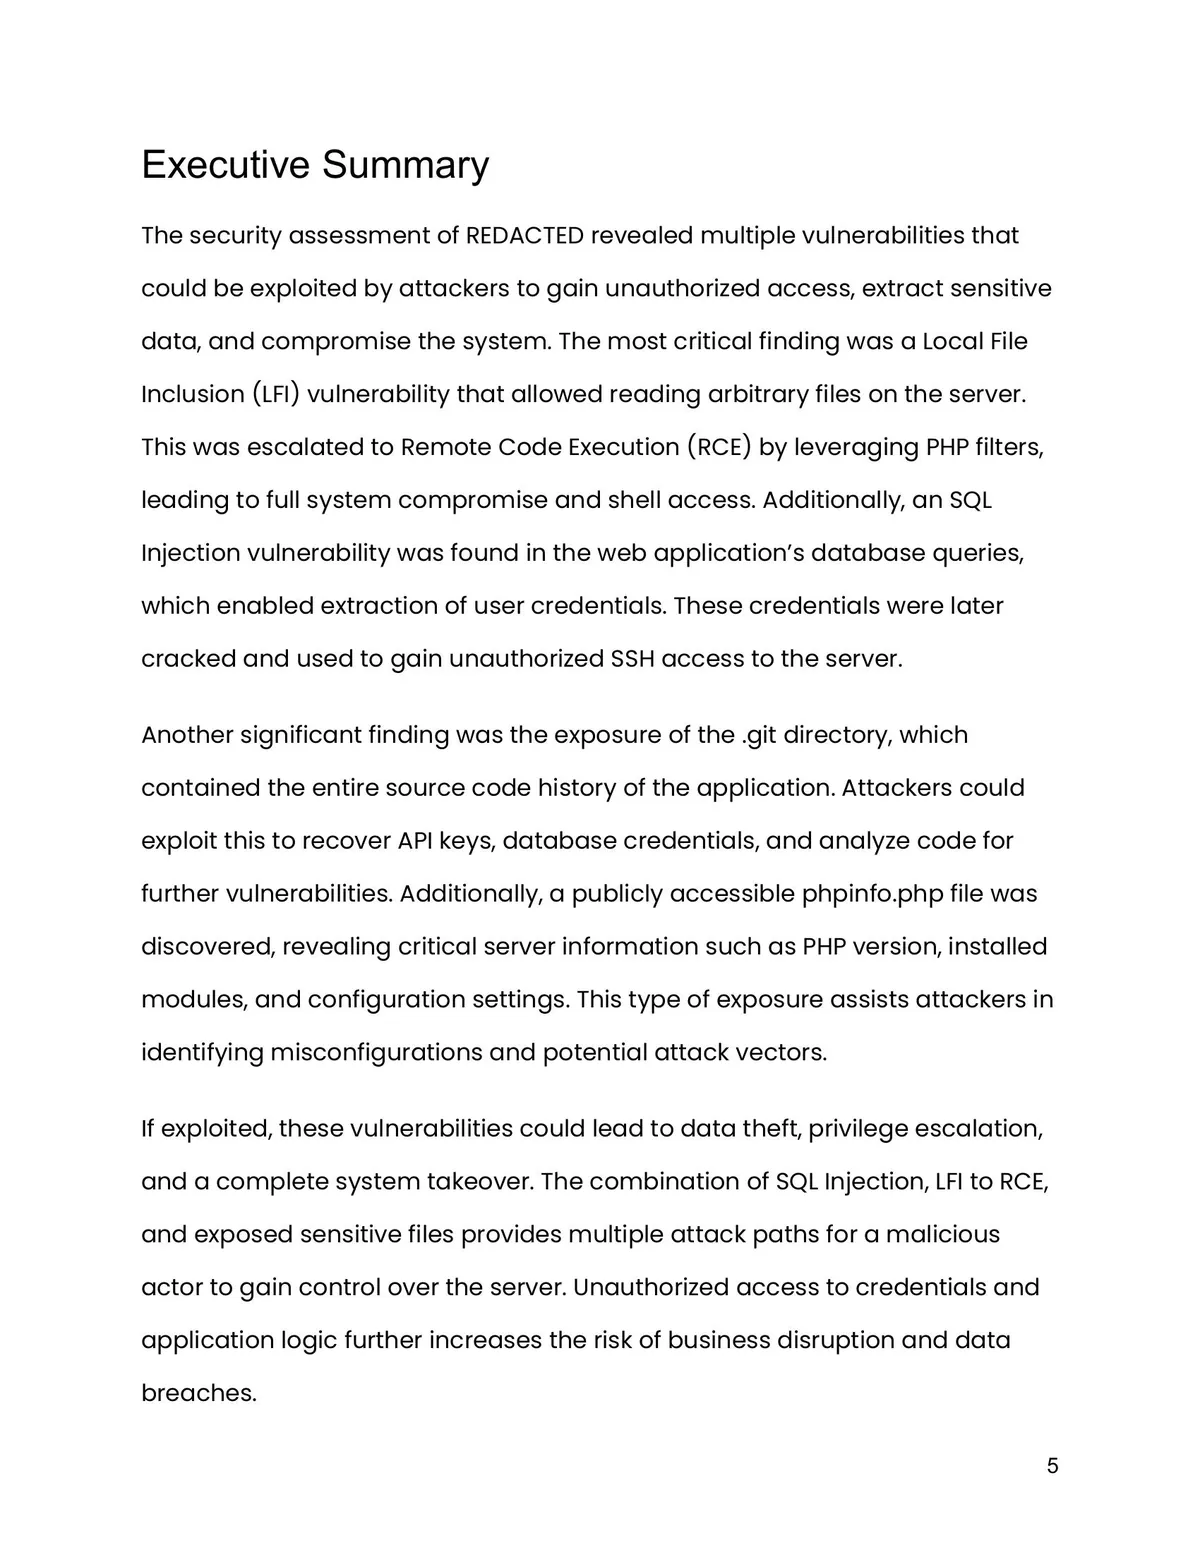
    Cover page of a StealthNet penetration testing report, marked sampleA report page describing one finding with details and the command to reproduce it
    What a Build hands you: a signed report with every finding written up and the steps to reproduce it. Sample shown.

    Run

    Subscription. Per covered app or environment.

    app.stealthnet.ai
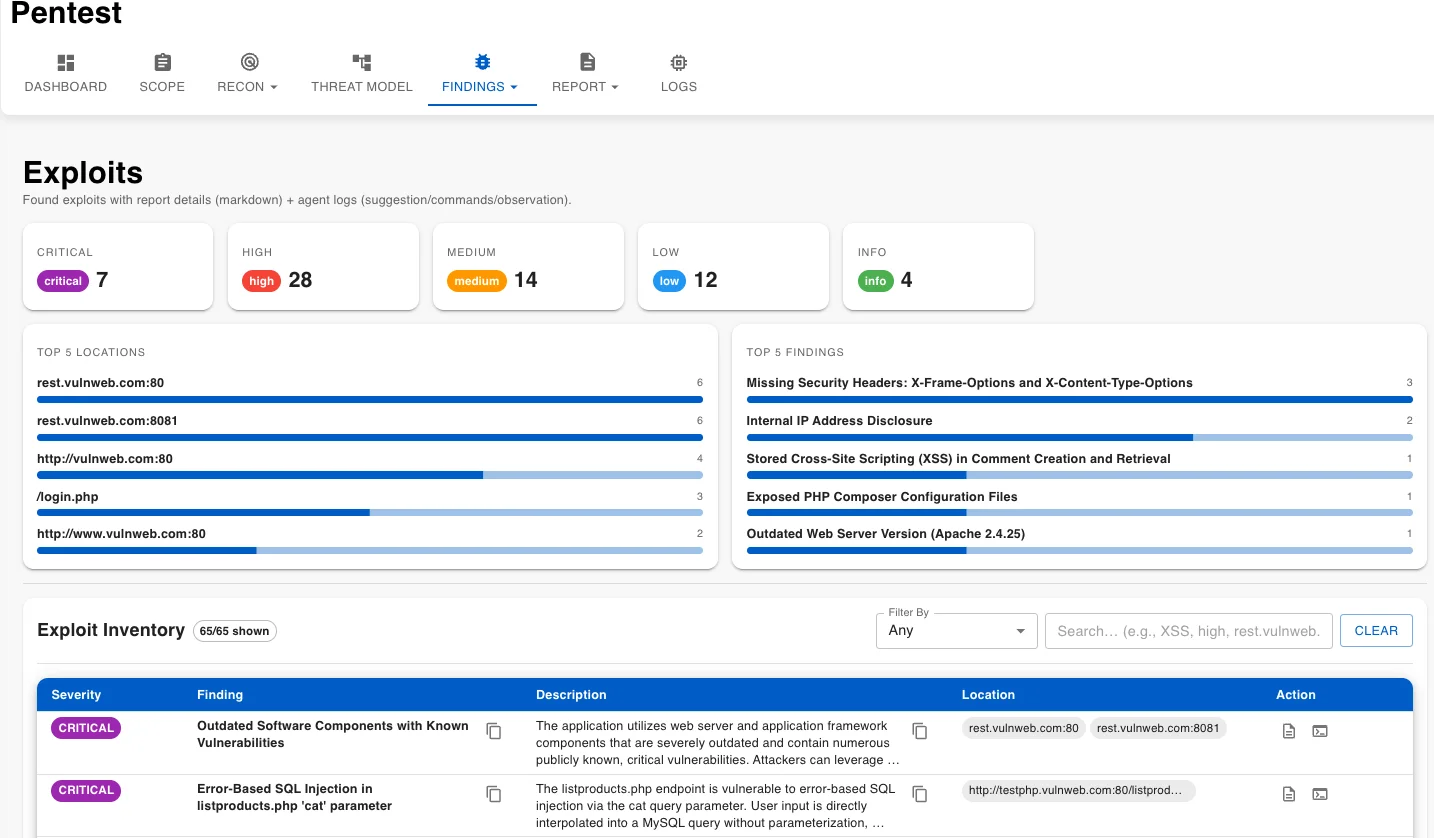
    StealthNet findings dashboard with severity counts, top locations and an exploit inventory
    Every monthly test lands in one findings view, with severity counts and an exploit inventory. Screen from the StealthNet platform.

    Starts from your Build and replaces the annual pentest for that app.

    • Core

      Up to 30 endpoints, 1 to 2 roles

      A senior tester review every quarter. Annual test at AI Pentest grade, ready for SOC 2 and ISO 27001.

      $7,500 per yearBilled annually

    • Growth

      31 to 75 endpoints, 3 to 5 roles

      Best for regulated apps

      2 senior tester hours every quarter. Annual test at Hybrid grade, with senior manual testing for FDA, PCI and multi-role apps.

      $15,000 per yearBilled annually

    • Program

      76 to 150 endpoints, 6 to 10 roles

      4 senior tester hours every quarter. Annual test at Hybrid grade, for complex platforms and APIs.

      $25,000 per yearBilled annually

    Every Run plan includes

    • A full AI pentest every month
    • A re-test on every release (up to four releases a month)
    • Unlimited retests on findings
    • A dated, full-scope annual test and signed report, timed to your audit window

    Prefer monthly billing? $750, $1,500 or $2,500 a month on a 12-month term. Release re-tests cover up to four releases a month. Extra senior tester hours are $250 per hour on any Build or Run. For PCI DSS, Run covers application and external testing; internal network and segmentation testing are scoped separately.

    How Build and Run fit together

    Do I need Run to buy a Build?
    No. A Build stands on its own: signed report, attestation letter, your test playbook and one retest.
    Can I start with Run?
    Run starts from a Build, which sets the baseline and playbook Run tests against. Tested with StealthNet in the last 12 months? That counts.
    Does Run replace my annual pentest?
    For SOC 2, ISO 27001 and HIPAA evidence, yes: ahead of each annual audit you get a dated, full-scope test and a fresh signed report, so you never buy a second Build for the same app. PCI internal and segmentation testing, and FDA premarket submissions, are scoped as their own test.
    What if our scope grows?
    We move you up a tier at renewal or whenever you ask. Unused senior hours roll over within your 12-month term.

    Pricing, timing and testing questions

    How much does continuous penetration testing cost?
    With StealthNet AI, year one is a Build plus Run. For one SOC 2 SaaS app that is typically $11,000: a $3,500 AI Pentest, then Run Core at $7,500 per year. Run Growth is $15,000 and Run Program is $25,000 per year. A traditional firm can charge $20K+ for a single annual test.
    How long does a penetration test take?
    An AI Pentest takes 48 hours from kickoff, report included. A Hybrid test takes 3 to 5 days. You get a fixed quote within 24 hours of your scoping call.
    How often should you run a penetration test?
    At least once a year and after any significant change. That is what most SOC 2 auditors look for, and what PCI DSS requirement 11.4 asks for. Run tests every month and re-tests every release, so changes are covered when they ship. See our SOC 2, PCI DSS, HIPAA and FDA 510(k) pages for each framework.
    Can our team run the AI agents ourselves?
    Yes. The StealthNet AI platform gives your team the same agents on a team license, from $6,000 per year with unlimited users. Run is the done-for-you version, with senior testers and a signed report.

    Add to any Run: vishing simulation, dark web monitoring and OSINT, quoted with your scope. Want to run the agents yourself? The self-serve StealthNet AI platform starts at $6,000 per year with unlimited users.

    What customers say

    ★★★★★ Rated 5.0 out of 5 on Capterra. Verified reviews.

    “The testing was thorough and the reports were structured precisely for the regulatory requirements. Explanation of issues along with steps to reproduce and remediation advice were detailed and clear, making corrections a breeze.”

    Jeremy M.

    Director, IKO Corp. Medical devices.

    “StealthNet AI performed a thorough and comprehensive pen test, fast turnaround on conducting the test, they were very responsive, and it was great value.”

    Richard B.

    Founder, Avara Software. Health, wellness and fitness.

    Trusted by Companies Where Security Isn't Optional

    TopLeft logo
    Derma Monitor logo
    Avara Software logo
    Omniscient Neurotechnology logo

    Audit-ready guarantee

    If your auditor or reviewer rejects a StealthNet report for the frameworks and scope in your statement of work, we rework it and retest at no extra cost.

    Close out this year signed. Start next year already running.

    Pick the setup closest to yours to see what year one looks like. Then book a 30-minute scoping call and get your own fixed quote within 24 hours.

    1. 1.
      Book a 30-minute scoping call

      Tell us what the app is and what the audit needs.

    2. 2.
      Get one fixed number per line

      Your quote arrives within 24 hours, agreed before any work starts.

    3. 3.
      Build, then Run

      Run begins when your Build report is delivered.

    What needs testing?
    Build: AI Pentest$3,500
    Run: Core, 12 months$7,500
    Year one$11,000

    Then $7,500 per year, next audit report included.

    ★★★★★ 5.0 on Capterra

    Examples for planning. Your quote is one fixed number per line, agreed before any work starts. Only need the Build? It stands on its own.

    Prices in USD, exclusive of applicable taxes. Valid through March 31, 2027. Build invoiced at signing. Run billed annually, or monthly on a 12-month term.